A Policy Is Written in Plain English
A security lead writes the rule she wants: any request carrying sensitive data needs human approval. Compass generates the YAML, the policy check passes, and it goes live with an outcome of require approval.
Scale AI adoption without risking your brand, data, or compliance. Compass runs inside your cloud to enforce your organization policies on every agent action.
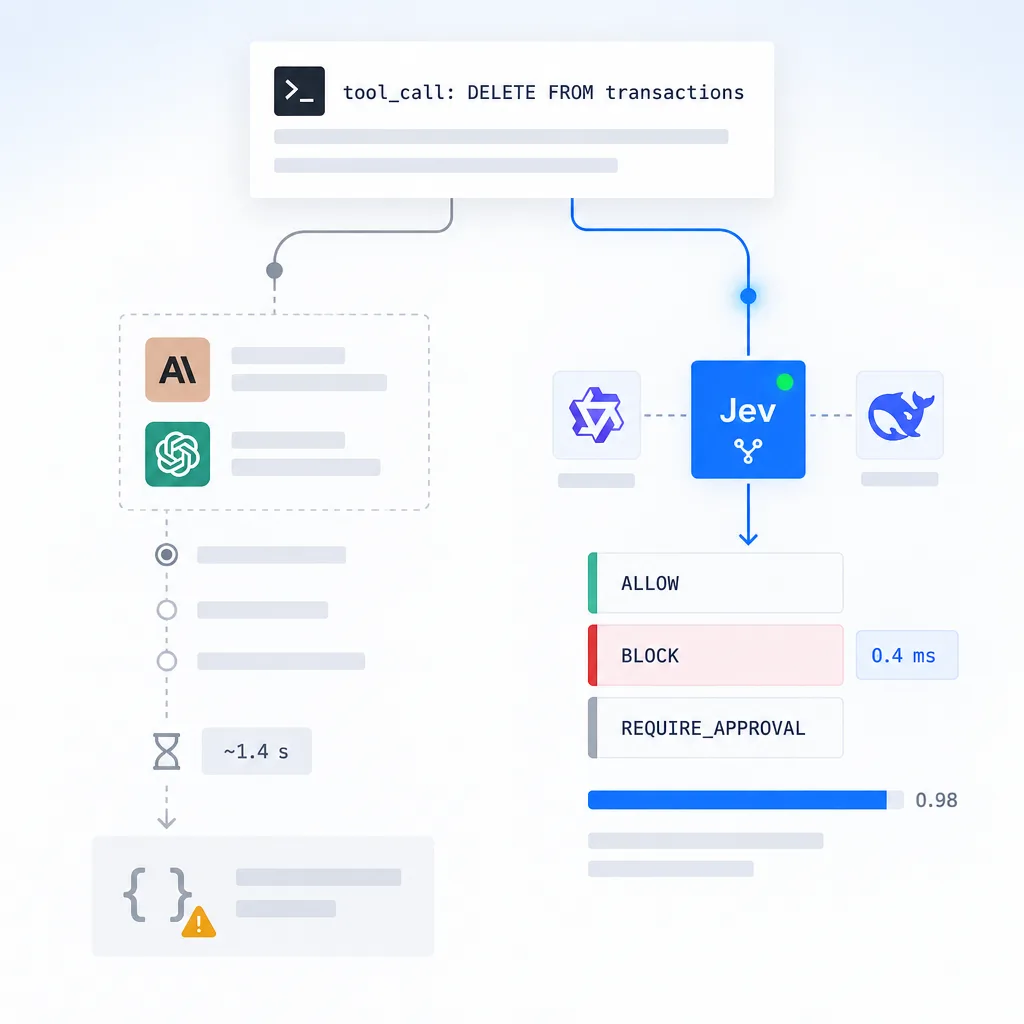
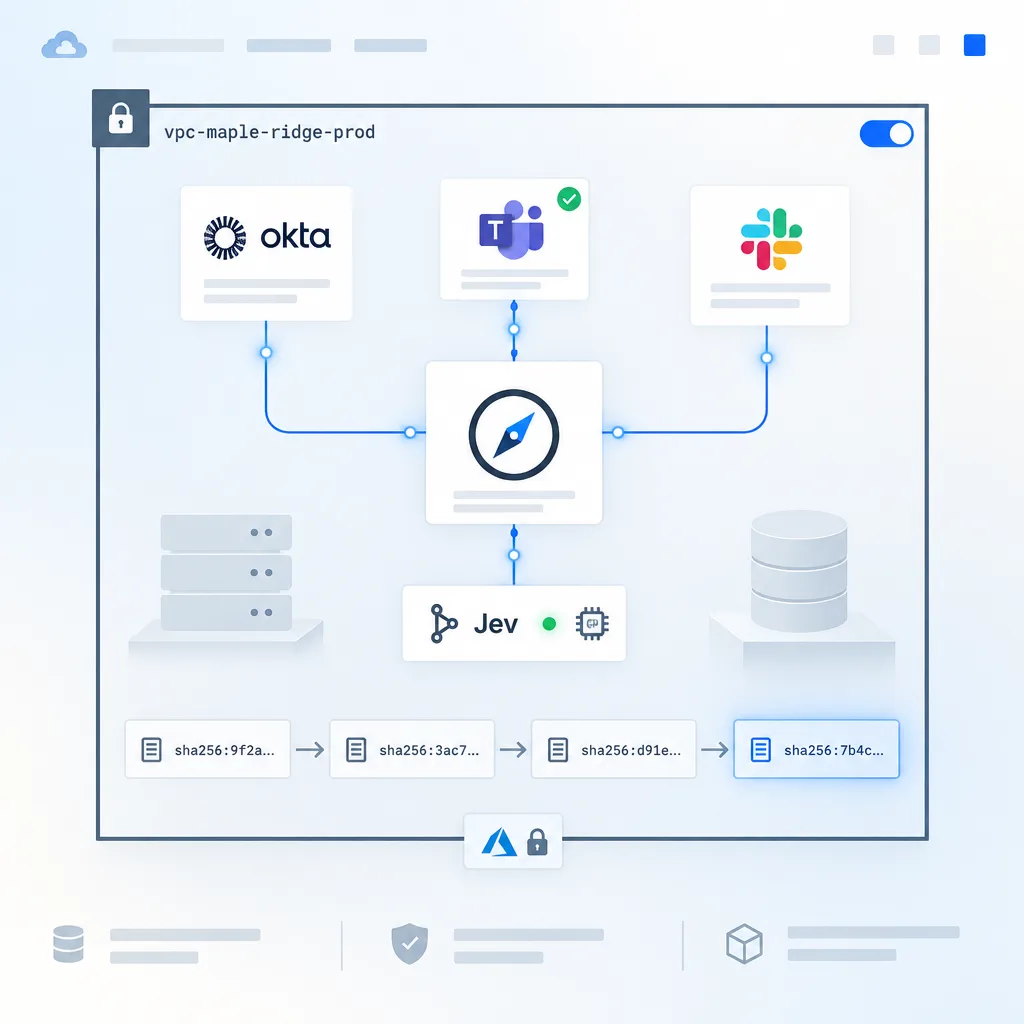
Compass is a governance agent. It sits in front of your AI agents and decides what each one may do at the moment it tries to act. Requests pass through Compass before they reach your systems.
Compass works with Kaji and with any other LLM-backed agent you run. Policies are authored in natural language or YAML, versioned like code, and applied to every agent on every team. Nothing about your agents' workflows has to change.
A policy engine, an approval step, and a log that cannot be edited.
Policies are written in YAML. Each rule sets one outcome for a request: allowed, blocked, or held for approval. Describe a rule in a sentence, and Compass writes the YAML, checks it for errors, and shows the effect before the policy goes live.
When a policy calls for approval, Compass stops the request before it runs. The approver sees which agent made the call, the exact action, and the context around it, then approves or rejects it. Approval requests arrive in Slack or in the Kaji chat.
Every decision is added to a hash-chained log: the policy that matched, the outcome, the approver, and the time. Each entry carries the hash of the entry before it, so any edit to an earlier record is visible immediately.
A security lead writes the rule she wants: any request carrying sensitive data needs human approval. Compass generates the YAML, the policy check passes, and it goes live with an outcome of require approval.
A developer asks an agent for the financial transaction reports sitting in a home directory. Compass matches the request against the active policy, holds it, and routes an approval request to the owner of that data.
The approver approves and the agent picks the work back up. The log captures the actor, the action, the outcome, and the hash. A separate policy blocks destructive commands such as rm -rf or DROP TABLE with no approval offered.
Policy checks run on Jev-class models. They are small and open source, and they are built for single-step decisions. A check returns one of three outcomes with a confidence score in well under a millisecond. Requests that need deeper reasoning go to a larger model, so the common case stays fast.
Compass deploys inside your VPC, your private cloud, or an air-gapped network. It reads identities from your identity provider, so approvals follow the groups and roles you already maintain. Prompts, policy decisions, and audit records are written to storage you control and stay there.
Compass runs inside your own cloud boundary or in a fully disconnected network. Prompts, policy context, and audit records stay on your infrastructure.
Approvals route to the roles you already define. Access to policies, approvals, and audit records follows the SSO and RBAC you run today.
Filter the trail by actor, action, or outcome, then export it as the evidence a compliance or incident review asks for.
Trademark Disclaimer: All third-party trademarks, logos, and brand names displayed on this website are the property of their respective owners. Any company, product, or service names used on this website are for identification and compatibility purposes only. Reference to these names, logos, or brands does not imply endorsement, sponsorship, partnership, certification, or affiliation with Shakudo, unless expressly stated.